
Business
Standard Operating Procedures: A Template for Any Business

A Standard Operating Procedure is the most practical document a business can produce — specific enough to guide independent execution, complete enough to maintain consistent quality across different team members and different time periods, and structured enough to be updated without rebuilding from scratch when processes evolve. Most businesses understand SOPs conceptually but struggle to implement them consistently because the gap between knowing what an SOP should accomplish and knowing how to write one that actually works is larger than it appears. This article provides a universal template and the practical guidance to apply it across any business process in any industry.
What Makes an SOP Actually Work
The difference between an SOP that sits in a shared drive unread and one that team members genuinely use is specificity. Generic process descriptions — “respond to customer inquiries promptly and professionally” — provide no operational guidance that a team member without prior context could apply. A working SOP provides enough detail that an intelligent person performing this task for the first time produces output indistinguishable from that of someone who has performed it a hundred times.
That specificity standard is demanding — and deliberately so. The effort required to write a genuinely specific SOP is the effort that converts institutional knowledge into organizational infrastructure. Every hour invested in writing a truly operational SOP saves multiples of that time in training, correction, and inconsistency management over the months and years the document is in use.
Understanding the operational management terminology that governs SOP development — process mapping, work instructions, quality standards, RACI, and version control — is essential for building a process library that serves the organization rather than satisfying an administrative requirement. A resource like Full Form Guide decodes the operational and quality management abbreviations that appear throughout SOP development guides, ISO documentation frameworks, and operational excellence resources — ensuring your SOPs are built on correctly understood process concepts rather than casually applied operational vocabulary.
The Universal SOP Template
The following template applies to any repeatable business process — service delivery, administrative functions, customer communication, financial processes, or operational tasks. Adapt the field names to match your industry’s language and your organization’s conventions, but maintain all structural elements for maximum utility.
[PROCESS NAME]
Use a specific, descriptive title that distinguishes this process from all others in your library. “New Client Onboarding — Discovery Call Scheduling” rather than “Client Scheduling.”
Document Information
- SOP Number: [Sequential identifier for library organization]
- Version: [Current version number — start at 1.0]
- Effective Date: [Date this version becomes the operating standard]
- Last Reviewed: [Date of most recent accuracy verification]
- Next Review Date: [Scheduled date for next accuracy check]
- Document Owner: [Role title — not person name — responsible for maintaining this SOP]
- Approved By: [Role title of person who approves this version]
Purpose
One to three sentences describing why this process exists and what organizational outcome it produces when executed correctly. Write this from the organization’s perspective — not the performer’s.
Example: “This SOP ensures that every new client receives a consistent, professional onboarding experience that establishes clear expectations, delivers initial value, and reduces early disengagement. Consistent execution of this process directly affects client retention rates and initial satisfaction scores.”
Scope
Define precisely what situations this SOP applies to and — equally important — what situations it explicitly does not apply to. Ambiguous scope is the primary source of SOP misapplication.
Example: “Applies to all clients who have signed a service agreement and made an initial payment. Does not apply to trial engagements, pilot programs, or prospects who have expressed interest but not yet signed. For trial engagement onboarding, see SOP-047.”
Process Owner
The specific role — not person — responsible for ensuring this process is executed correctly and that this SOP remains accurate. Attaching ownership to roles rather than individuals prevents ownership gaps when personnel changes occur.
Roles and Responsibilities
List every role involved in this process and what each is responsible for. A RACI matrix format — Responsible, Accountable, Consulted, Informed — works well for multi-person processes.
| Role | Responsibility in This Process |
|---|---|
| [Role 1] | [Specific responsibilities] |
| [Role 2] | [Specific responsibilities] |
| [Role 3] | [Specific responsibilities] |
Inputs Required
Everything that must exist or be available before this process can begin:
- Information required: [Specific data, documents, or completed prior process outputs]
- Tools required: [Specific software, equipment, or physical materials]
- Access required: [Systems, accounts, or permissions needed]
- Prerequisites: [Other processes that must be completed first — with SOP reference numbers]
Outputs Produced
Everything this process produces when completed correctly:
- Primary output: [The main deliverable or outcome]
- Secondary outputs: [Supporting documents, notifications, or records created]
- Downstream triggers: [Processes or activities initiated by completion of this process]
Step-by-Step Instructions
This is the core of the SOP — the sequential instructions that guide execution from start to finish. Write each step as a specific action in the imperative voice. Number every step. Include decision points explicitly — “If [condition], go to Step X. If [condition], continue to Step Y.” Add screenshots, annotated images, or video links for steps that involve visual interface navigation or physical procedures where images communicate more clearly than text.
Step 1: [Specific action — tool, location, and exact action. “Log into [specific platform] at [URL] using your assigned credentials. Navigate to [specific menu path].”]
Step 2: [Next specific action]
Step 3: [Decision point if applicable. “If the client account shows [status], proceed to Step 4. If the account shows [different status], follow the exception procedure in Section 9 and restart from Step 1.”]
Step 4: [Continue through all steps to process completion]
Final Step: [The specific action that signals process completion — closing a ticket, sending a confirmation, updating a record, or completing a quality check.]
Quality Standards
Define what correctly completed output looks like — the standard against which execution can be verified.
Example: “The completed onboarding email must: include the client’s name spelled exactly as it appears in the signed agreement; link to the correct onboarding resource for their specific service tier; be sent from the designated onboarding account rather than a personal inbox; and be sent within 4 business hours of signed agreement receipt.”
Study how successful consumer brands like Colour Pop maintain consistent quality across complex operations — product development, packaging, community engagement, and customer communication — executed by teams rather than founders. That consistency is the product of documented quality standards that define what excellent looks like specifically enough that anyone can evaluate whether a given output meets them. The same standards-based quality infrastructure is available to any business willing to invest in defining and documenting what excellent actually means for each process it executes.
Timelines and Deadlines
Specify when each step should be completed relative to the process trigger:
- Process initiation: [Triggering event + time requirement. “Must begin within 2 hours of signed agreement receipt.”]
- Step-specific deadlines: [For steps with their own timing requirements]
- Process completion: [Maximum time from initiation to final step]
Common Errors and How to Avoid Them
Document the mistakes that most frequently occur when this process is executed — based on historical performance, quality audits, or the practitioner’s experience — with specific prevention actions for each.
| Common Error | Why It Happens | Prevention Action |
|---|---|---|
| [Specific error 1] | [Root cause] | [Specific prevention] |
| [Specific error 2] | [Root cause] | [Specific prevention] |
| [Specific error 3] | [Root cause] | [Specific prevention] |
Exception Handling
Define what to do when the standard process doesn’t fit the situation — the conditions that represent exceptions, who has authority to handle them, and what the alternative process looks like.
Example: “If the client’s service agreement includes custom terms not covered in the standard onboarding package, escalate to the Account Manager before proceeding. Do not proceed with standard onboarding until the Account Manager confirms which steps apply to the custom agreement.”
Escalation Path
Define who to contact when the process encounters a situation not covered by the instructions or exception handling guidance — what information to provide, and what to do in the interim while waiting for guidance.
- First escalation: [Role title] via [contact method] with [specific information to include]
- Second escalation (if first unavailable): [Role title] via [contact method]
- Interim action while awaiting escalation response: [Specific holding action]
Related Documents and Resources
- Related SOPs: [Links or reference numbers for SOPs that connect to this one]
- Templates used: [Links to any templates referenced in the instructions]
- Tools documentation: [Links to user guides for tools referenced in the process]
- Training materials: [Links to any training resources that support this SOP]
Record Keeping
Specify what records must be created when this process is executed, where they are stored, and how long they are retained.
- Records created: [Specific record types]
- Storage location: [Specific system and folder path]
- Retention period: [Specific timeframe, governed by any applicable regulations]
- Access permissions: [Who can view, edit, or delete these records]
Version History
| Version | Date | Author | Changes Made |
|---|---|---|---|
| 1.0 | [Date] | [Name/Role] | Initial document |
| 1.1 | [Date] | [Name/Role] | [Specific changes] |
Adapting the Template to Your Process Type
The template above covers all structural elements needed for any process — but different process types require different emphasis in implementation.
Customer-facing processes: Emphasize tone and quality standards. Document not just what to do but how to communicate — the specific language, format, and response timing that defines the customer experience your brand delivers. Every customer interaction is an expression of brand identity, and the SOP is the mechanism that makes that expression consistent across team members.
Financial processes: Emphasize controls and verification steps. Document the specific reconciliation checks, approval requirements, and error detection mechanisms that prevent financial errors from compounding before detection. Financial SOPs should include explicit authorization requirements at each stage where financial commitments are made.
Technical processes: Emphasize screenshots, annotated images, and specific interface navigation. Technical processes with visual interfaces — software configuration, platform management, tool operation — communicate more accurately through images than through text descriptions of interfaces the reader hasn’t yet seen.
People processes: Emphasize judgment guidance and escalation paths. Processes involving human relationships — hiring, performance management, conflict resolution — require decision frameworks and escalation criteria more than sequential instructions because the situations they address are inherently variable and context-dependent.
Implementation: Getting SOPs Used Rather Than Filed
An SOP library that exists but isn’t used is worse than no library — because it creates the organizational impression that process documentation exists while providing none of the operational benefit that actual documentation use produces.
Building a documentation culture where team members genuinely use SOPs requires deliberate implementation choices.
Make SOPs the first resource: When a team member asks how to perform a task that has an SOP, the correct response is “That’s documented — here’s the link” rather than a verbal explanation that bypasses the SOP. Every verbal explanation that replaces an SOP reference teaches team members that the SOP isn’t the real answer — which makes the documentation an administrative artifact rather than an operational tool.
Update SOPs before implementing changes: Process changes that aren’t reflected in the SOP immediately create a gap between documented and actual practice that invalidates the document for every team member who follows it. The discipline of updating the SOP before implementing the change — rather than intending to update it afterward — maintains the library’s accuracy and the team’s trust in its reliability.
Reference SOPs in onboarding explicitly: New team members who are directed to specific SOPs as their primary learning resource for each process develop the habit of consulting the process library before asking questions — which both accelerates their independence and maintains the SOP’s function as the organizational knowledge repository rather than a backup resource for when the experienced team members aren’t available.
Audit against SOPs regularly: Periodic quality audits that compare actual practice to documented practice identify both performance gaps — where team members aren’t following documented procedures — and documentation gaps — where documented procedures no longer match actual best practice. Both types of gaps require correction; the audit distinguishes which type is present in each situation.
Digital Compliance in Process Documentation Systems
Process documentation systems — knowledge bases, wiki tools, and SOP management platforms — that connect to your business website or process personal data through web-based interfaces generate privacy compliance obligations under GDPR, CCPA, and other applicable regulations. Any processes that involve collection or handling of personal data must include explicit data privacy steps in their documentation — specifying what data is collected, how it is stored, who can access it, and how long it is retained.
A platform like Cookiebot automates cookie consent management across your website and generates the compliance documentation that makes data collection processes auditable under applicable privacy regulations. Referencing this compliance infrastructure in the SOPs for every process that involves digital data collection ensures that every team member executing those processes understands the privacy obligations embedded in them — converting compliance from an organizational aspiration into an operational standard embedded in the process documentation every team member follows.
The Bottom Line
A Standard Operating Procedure is simultaneously the most practical and most undervalued document a business produces. It converts institutional knowledge into organizational infrastructure, makes training faster and more consistent, enables quality management at scale, and provides the foundation for genuine delegation — because you cannot effectively delegate work whose standards aren’t defined in writing. The template provided in this article applies to any process in any business. The discipline required to complete it for every critical process your business executes is the discipline that separates businesses that scale consistently from those that grow chaotically — adding people and complexity without adding the operational coherence that makes growth sustainable.
Every company in the defense supply chain handles information the government wants protected, from technical drawings to contract details. Two frameworks shape how that protection works: the Defense Federal Acquisition Regulation Supplement (DFARS) and the Cybersecurity Maturity Model Certification (CMMC). They are closely linked, but they serve different purposes. Many contractors turn to CMMC consulting services to sort out where one ends and the other begins. A clear view of both frameworks makes it easier to protect sensitive data and stay eligible for defense work.
What DFARS Requires
DFARS adds DoD-specific rules to the broader federal acquisition process. For cybersecurity, it requires contractors to meet an established set of security standards, report cyber incidents to the DoD within a short window of discovery, preserve records of affected systems for a set period, and ensure that any cloud providers storing covered data meet recognized federal security standards.
The Role of Security Standards
A widely recognized cybersecurity framework serves as the technical foundation for both DFARS and CMMC. It covers over a hundred security requirements organized into categories such as access control, incident response, configuration management, and system integrity.
For years, many contractors self-reported their compliance with these requirements without independent verification. That gap in accountability was a key reason the CMMC program was developed.
Understanding the Types of Sensitive Information
Both frameworks focus on two types of information. The first is basic federal contract information, which is non-public data created or shared under a government contract. The second is more sensitive and includes information that requires stronger protections under law or policy, such as export-controlled technical data or certain engineering specifications.
Handling sensitive information correctly means knowing where it lives, who can access it, and how it moves. Proper labeling, encryption, access restrictions, and secure disposal are all part of responsible data management. The type of information a contractor handles generally determines what level of compliance is required.
CMMC Compliance Levels
CMMC organizes requirements into three levels:
- Level 1 (Foundational): Covers basic federal contract information with a small set of safeguarding requirements. Contractors complete a regular self-assessment to confirm compliance.
- Level 2 (Advanced): Applies to contractors handling more sensitive information and aligns with a comprehensive set of security controls. Most contracts at this level require a third-party assessment by an authorized organization on a recurring basis.
- Level 3 (Expert): Applies to the most sensitive defense programs and adds requirements beyond the standard framework. Government assessors perform these reviews directly.
All levels require a senior company official to affirm continued compliance on a regular basis.
How the Two Frameworks Intersect
The simplest way to see the relationship: DFARS sets the requirements, and CMMC verifies them. DFARS has long required contractors to meet established cybersecurity standards. CMMC adds a formal process to confirm that contractors actually follow through.
As the program matures, contracting officers can require a specific CMMC level as a condition of winning a contract. It’s important to note that CMMC does not replace DFARS obligations. Incident reporting, cloud security requirements, and other DFARS rules still apply alongside certification.
How DFARS and CMMC Work Together
DFARS and CMMC function as two halves of one system. DFARS defines what contractors must do to protect sensitive government information, while CMMC confirms that those protections are actually in place. As CMMC requirements appear in more defense contracts, certification status will become a routine factor in contract awards. Contractors who understand the security standards, handle sensitive information responsibly, and know their required compliance level will be well positioned as these frameworks continue to evolve.
Cybersecurity problems rarely show up as one big failure. They usually appear as friction: an insurance renewal that gets harder every year, a security hire who leaves after eight months, or a dashboard full of alerts no one has time to read. Each issue looks manageable alone. Together, they suggest your security model has stopped keeping up with your business. A managed cybersecurity provider brings dedicated people, mature processes, and continuous oversight to fill those gaps. The five signs below can help you judge where your organization stands.
1. Your Security Tools Generate More Noise Than Action
Many companies respond to new threats by buying new tools. Over time, that creates a stack of antivirus software, firewalls, email filters, and cloud monitoring platforms that don’t talk to one another. Each one sends its own alerts, often hundreds per day.
When no one has time to sort real threats from false alarms, important warnings get buried. Industry studies regularly show that many alerts are never investigated at all. Owning advanced technology means little if no one is tuning it, connecting the data, and acting on what it finds. If your team has started ignoring notifications, your tools are working harder than your defenses.
2. You Can’t Hire or Keep Security Talent
Experienced security analysts are in short supply, and larger enterprises can usually outbid smaller firms on salary. Even when you land a strong candidate, retaining them is another challenge. A single security employee often burns out from being on call every night and weekend.
When that person leaves, they take critical knowledge with them, such as how systems are configured, where the weak spots are, and which vendors have access. If your security program depends on one or two people, a single resignation can leave you exposed for months while you search for a replacement.
3. Cyber Insurance Is Getting Harder to Secure
Insurers have tightened their requirements sharply in recent years. Renewal applications now ask detailed questions about multi-factor authentication, endpoint detection, privileged access controls, and backup testing. Vague answers can lead to higher premiums, lower coverage limits, or outright denial.
If your latest renewal raised costs significantly or flagged missing controls, treat that as an outside expert’s assessment of your risk. Insurers have studied thousands of claims. When they question your security posture, they are pointing to the same gaps attackers tend to exploit.
4. You Don’t Have a Tested Incident Response Plan
Some businesses have a response plan stored in a shared folder. Few have practiced it. When an attack happens, confusion spreads fast. Who shuts down affected systems? Who contacts legal counsel, customers, or law enforcement? Which backups are clean?
Without clear roles and rehearsed steps, teams lose valuable hours making decisions under pressure. Those hours often decide whether an incident stays contained or turns into a costly, weeks-long recovery. A plan that has never been tested is closer to a hope than a strategy.
5. Leadership Can’t Answer Basic Risk Questions
Boards, investors, and executive teams increasingly expect clear answers about cyber risk. How exposed is the company? What are the top threats? How quickly could operations recover from an attack? If those questions lead to guesswork or long pauses, decision-makers are operating without the information they need.
Security reporting should translate technical findings into business terms, including financial impact, operational risk, and progress over time. When leaders can’t see that picture, they can’t set priorities or budget wisely, and security becomes reactive instead of planned.
Signs Your Security Has Outgrown Its Resources
Each of these warning signs points to the same underlying issue: security demands have outgrown the resources assigned to them. Alert overload, talent shortages, insurance pressure, untested response plans, and unclear risk reporting all slowly erode a company’s ability to defend itself. Spotting these patterns early gives business leaders a more accurate view of their exposure. Strong security depends on more than tools. It relies on consistent expertise, clear processes, and visibility that reaches every level of the organization.
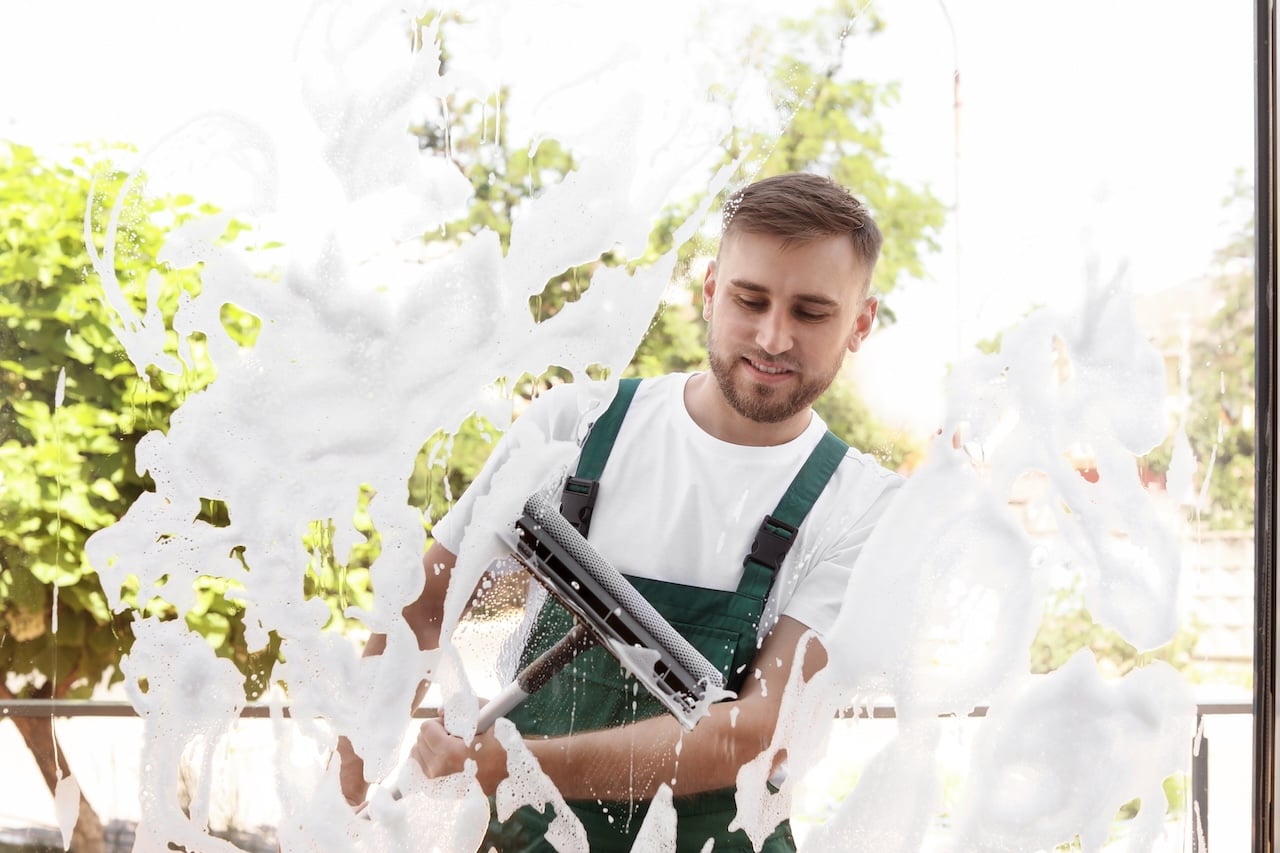
You spend an afternoon washing every window in the house or office, step back to admire your work, and then the sunlight hits the glass. Suddenly, streaks, smears, and cloudy patches appear everywhere. Streaky glass is one of the most common cleaning frustrations, and it often has little to do with effort. That’s a big reason professional window cleaning crews consistently deliver streak-free results for both residential and commercial properties: they control every factor with the right equipment and technique. Below are the most common causes and why so many homeowners and business owners choose to leave the job to the pros.
The Wrong Cleaning Solution
Many store-bought glass cleaners contain soaps, dyes, or ammonia that leave a thin film on the glass. Using too much product makes it worse, since the extra solution dries before you can wipe it away. For small DIY jobs, a few drops of mild dish soap in warm water works well. Professional cleaners use commercial-grade solutions formulated to lift dirt without leaving residue — a difference that shows on storefronts and office glass where first impressions matter.
Dirty or Low-Quality Squeegees
A nicked, worn, or dirty squeegee blade skips across the surface and leaves thin lines. Replace the rubber edge when it becomes rounded, wipe the blade after every stroke, and store it so the rubber isn’t pressed against hard surfaces. Professional cleaners use commercial-grade squeegees, replace blades regularly, and carry extension equipment for high windows — tools most homeowners and office managers don’t have on hand.
Cleaning in Direct Sunlight
Warm glass causes cleaning solution to evaporate before you can wipe it away, leaving soap and dirt behind. For DIY cleaning, work on overcast days or in the early morning. Professional crews schedule and sequence their work around sunlight and shade, which is one reason results are more consistent — especially on properties with large glass surfaces.
Hard Water Mineral Deposits
Tap water contains calcium and magnesium that dry on glass as white spots or a cloudy haze. Distilled or filtered water helps prevent new deposits. For existing buildup, a vinegar solution or mineral-removal cleaner can dissolve the staining. Professional cleaners carry specialized treatments for heavy deposits and can restore glass that looks permanently stained — a common problem on commercial storefronts and homes with irrigation systems near windows.
Dirty Cloths and Poor Technique
Cloths holding dirt, grease, or fabric softener spread residue across clean glass. Use lint-free microfiber, wash without fabric softener, and swap for a fresh cloth once it’s damp. Technique matters just as much: wiping in circles pushes dirt around, and skipping frames lets dirty water drip onto clean panes. Work top to bottom in straight, overlapping squeegee strokes, wipe the blade after each pass, and finish edges with a dry cloth.
The Value of Professional Window Cleaning
Whether you own a home or manage a commercial property, professionally cleaned windows offer more than clear glass. They let in more natural light and, for businesses, signal professionalism to every client who walks through the door. Regular service also extends window life. Dirt, mineral deposits, and oxidation wear down glass and seals over time. Catching those issues early costs far less than replacing windows — protecting home value for residential clients and keeping commercial buildings looking well-maintained year-round.
Final Thoughts
Streaks come down to a few fixable causes: residue-heavy cleaners, worn squeegees, dirty cloths, direct sunlight, hard water, and poor technique. Each is manageable with the right knowledge. But for homeowners who want lasting results without the trial and error, and for businesses where clean windows affect how customers see the property, professional window cleaning delivers consistency, safety, and care that’s hard to match on your own.

The Laboratory Report That Looks Complete Until Someone Checks the Sample: Why Independent Testing, Lot Identification and Analytical Limits Matter in Peptide Research Copy headline
Jaw Clicks But Doesn’t Hurt: Ignore It or Get It Looked At?

Your hair may have been decided before you were born: 287 genetic signals, one Huntsville genomics campus, and the question to ask of every hair-peptide claim

Retatrutide, Retatrutida, LY3437943: One Molecule, Three Names, and the Spelling Trap That Sends Spanish-Speaking Researchers to the Wrong Search Results
Crowded Teeth or a Bad Bite: The Difference That Decides Invisalign or Braces

Preventive Maintenance Checklist for Industrial Chillers

Why Play-Based Learning Helps Children Thrive

How to Furnish a Tiny Home Without Sacrificing Sleep

How Better Insulation Helps Your HVAC System
Standard Operating Procedures: A Template for Any Business
-
 Beauty7 years ago
Deep Breathing Techniques To Change Your Life
-
 Beauty7 years ago
Six Essential Food Items For Runners
-
 Featured7 years ago
There’s More To Weight Loss Than Dieting
-
 Beauty7 years ago
Healthy Choices To Help You Live Longer
-

 Beauty6 years ago
8 Ways to Prevent Acne Breakouts
-

 Featured6 years ago
Turn Your Extra Rice Into Something More
-

 Featured6 years ago
The Fur-Parent’s Guide to Caring for Your Dogs During and After a Lockdown
-
 Uncategorized7 years ago
Microsoft plans to reach negative carbon emissions by 2030 * Establishing $ 1 billion funds to find solutions